Identity Lifecycle Management
Automate and secure the entire identity lifecycle
Risk increases when lifecycle and access are misaligned. Describe how joiners, movers and leavers should be handled in plain language, and Linx automates the full lifecycle, from first-day provisioning to final-day deprovisioning, running every workflow accurately and immediately, every time.
Built for and trusted by leading enterprises


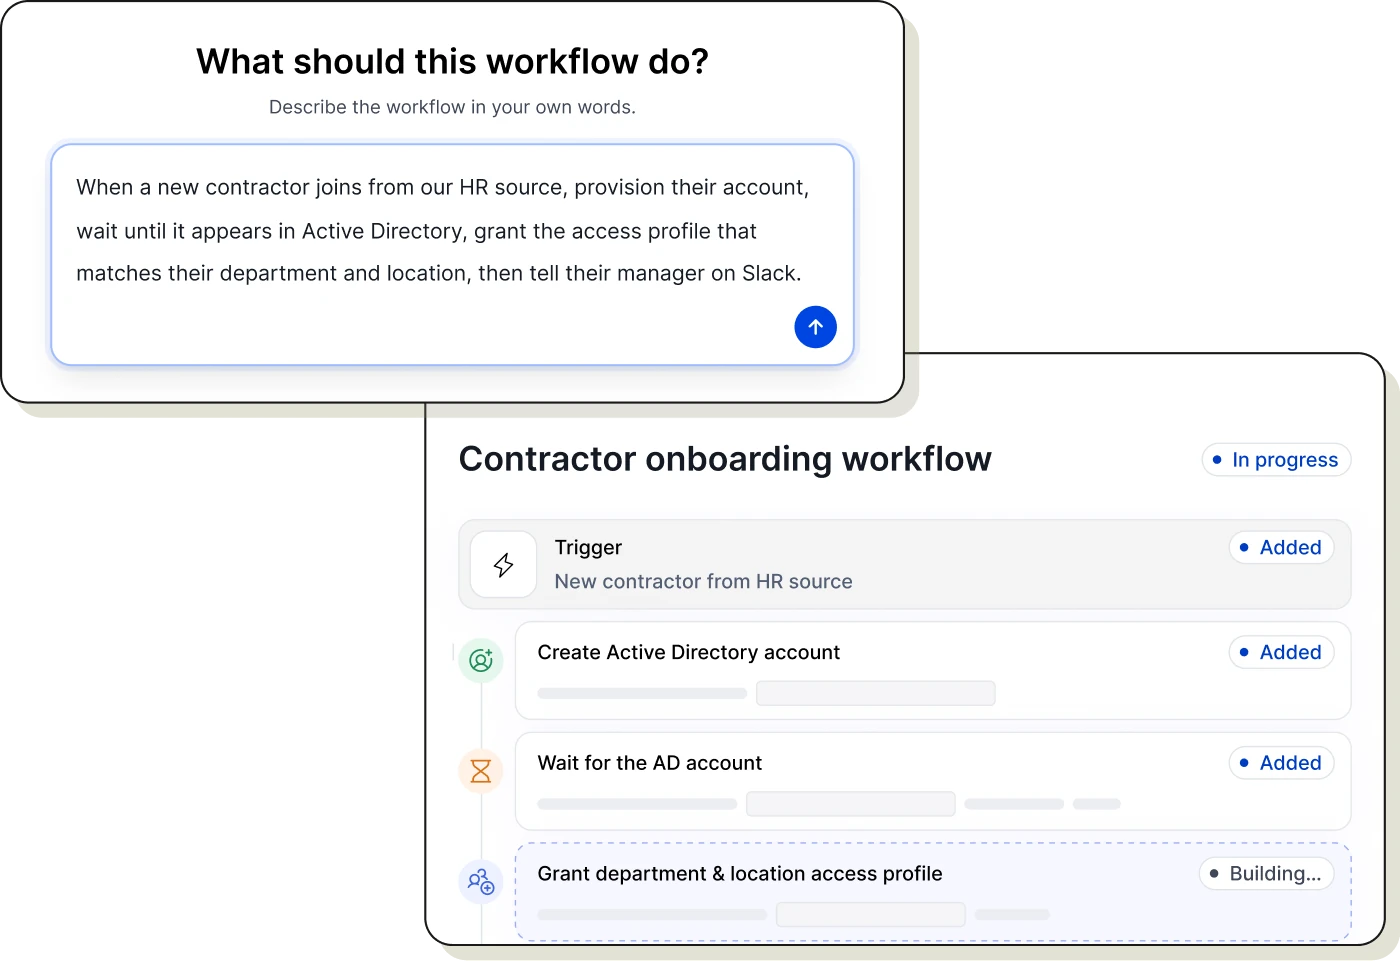
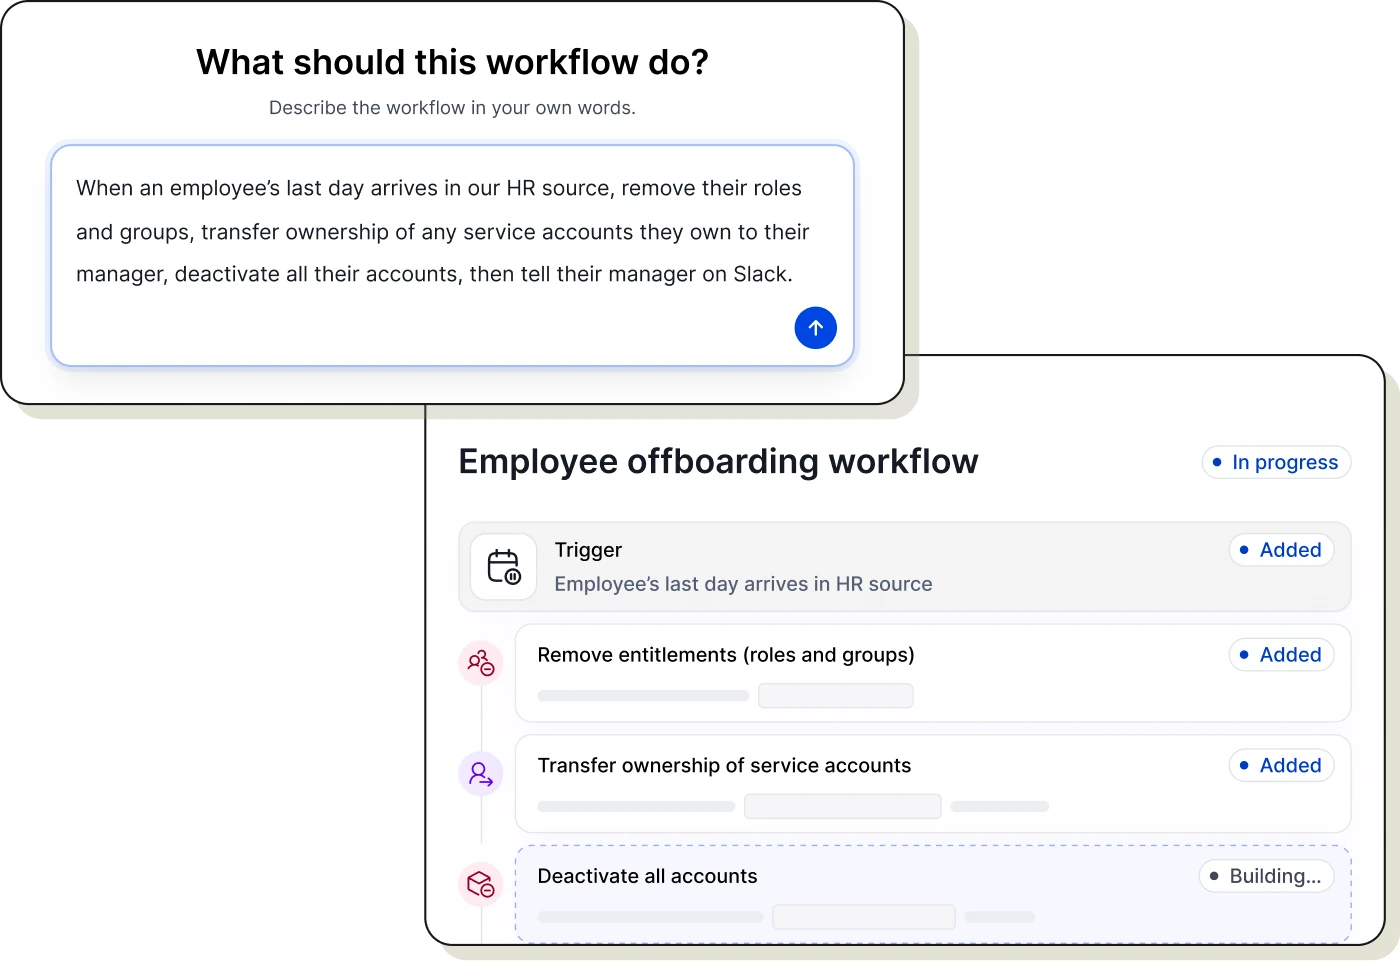
Say what you need. Linx builds the workflow.
Describe how a new hire, a team move or a departure should be handled, in plain language. Linx asks what it needs to know, builds every step, shows you the code behind it and lets you dry-run it before anything goes live. That way access is right at every stage of the lifecycle.
Every identity has a beginning, a middle, and an end. Govern all three.
Linx detects lifecycle changes and adjust access as needed - provisioning the right access from day one, adjusting it precisely when roles change, and removing it completely when employment ends.
Right access from day one
Enable users to request the access they need, when they need it via Slack, Teams, MCP, and a web portal. Automatically route each request to the right reviewers.
Access that keeps pace with role changes
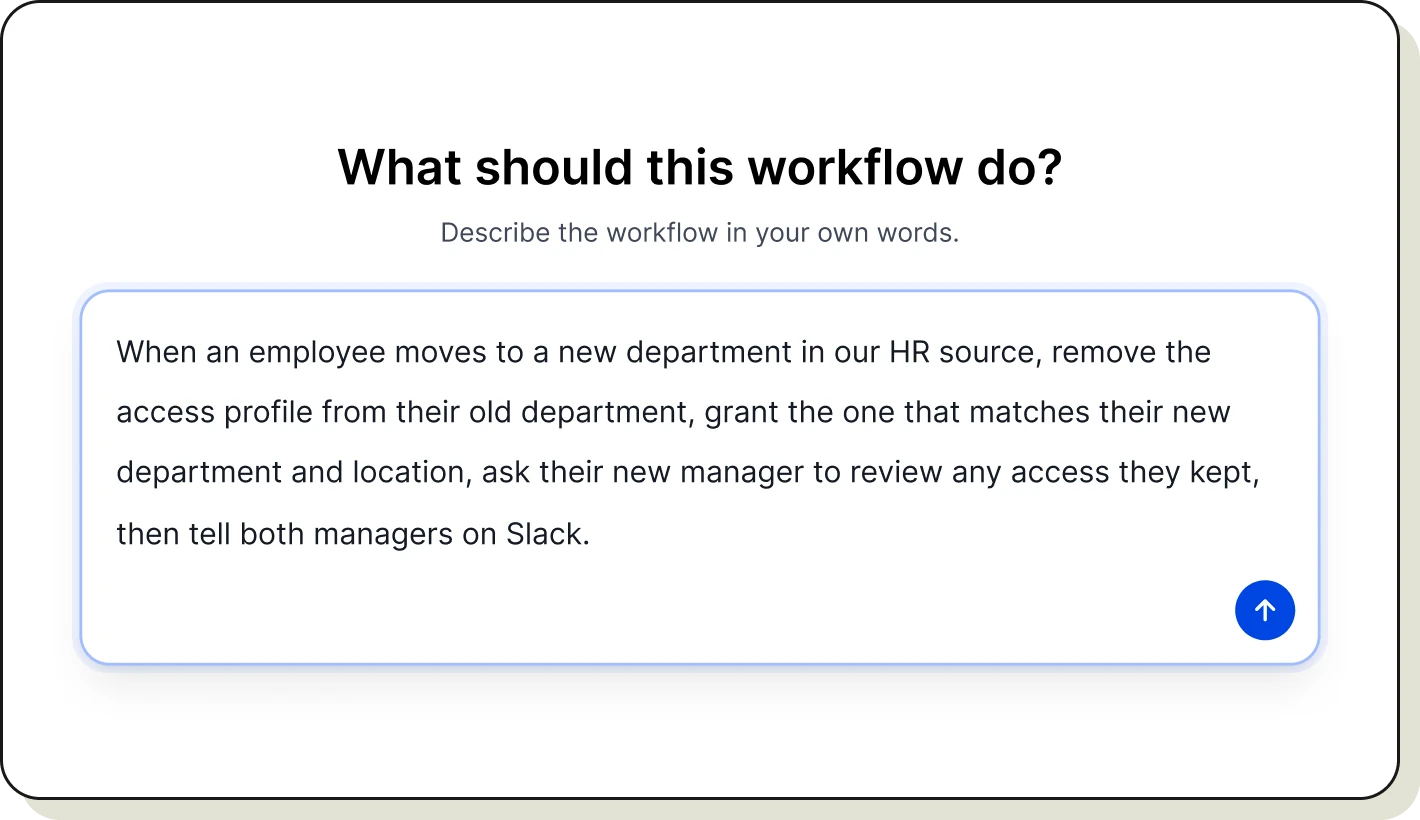
When someone changes roles or transfers to a new team, Linx detects it and automatically adjusts entitlements, granting new access aligned to the new role and removing access that no longer applies. No accumulation. No drift. No manual reconciliation.
Complete offboarding, every time
When someone leaves, Linx triggers a complete offboarding workflow: access revoked across every connected system, credentials deactivated, and the identity marked inactive in the Identity Graph. No orphan accounts. No residual access. No exceptions.
“As a former CRO of SailPoint, I am excited by Linx’s innovative approach to identity security and governance. Their use of cutting-edge technologies are truly revolutionizing the space and setting a new standard for the industry.”