Linx vs. C1
Pair governance with security context


How Linx and C1 differ
C1
Why leaders in IAM prefer Linx
“In a matter of weeks with Linx, we've been able to quickly identify risky accounts, risky privileges, and be able to automate the remediation of all of those things.”
“With Linx, we can remediate and take action when needed, allowing us to really save teams time by automating workflows so we could focus on things that really matter.”
“Linx gave us the visibility we didn't know we were missing. It wasn't just a dashboard. It actually did something.”
“Since implementing Linx, the data that we provide to auditors is just better. The process has improved. The amount of time to deliver evidence has improved exponentially.”
“We can see all the agents that are in use and what access they have to what application and data source. It is a full security and governance platform.”
“The implementation is straightforward, and allows us to gain meaningful visibility into identity risk much faster than expected.”
How Linx and C1 compare in practice
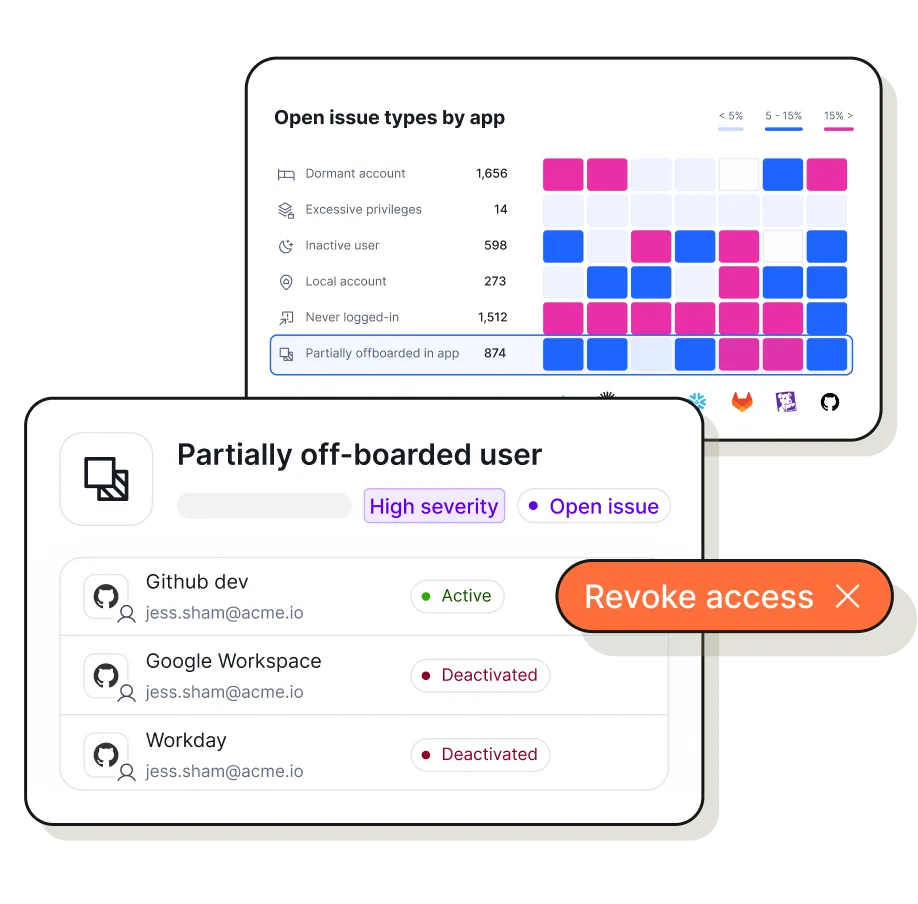
Linx pairs ISPM with no-code, in-platform remediation. When a risky entitlement, dormant account, or partial offboarding is flagged, the fix happens inside Linx through dynamic workflows, not a ticket to another team.

C1 can remediate access changes inside the platform, but there's nothing to prioritize or surface risks. Access revocations route through a ticket.
Linx AI runs in three layers: continuous data refinement beneath the platform, an assistant that carries context across every page (including your security posture, not just access), and autonomous agents through Linx Autopilot that detect, evaluate, and resolve without a human kicking it off.
C1's AI assistant is scoped to access reviews and requires separate workflow configuration. There's no natural-language interface for asking about your identity posture.
Linx governs service accounts, API keys, bots, and AI agents under the same policy engine as human identities through agentic identity governance, with the MCP Gateway controlling how AI agents reach the systems they act on and just-in-time access applied automatically.
C1's NHI coverage today is largely visibility — discovering service accounts and credentials — without a governance layer on top.
Linx treats ISPM as a continuous control. The platform maps every identity, entitlement, and resource on an ongoing basis and puts orphaned accounts, dormant users, admin sprawl, and missing MFA in front of you natively.
C1 has no security posture layer. There's no ability to flag orphaned accounts, dormant users, or MFA gaps without custom configuration.
Linx was built as an identity security and governance platform from the start. Access requests, certifications, user access reviews, and lifecycle policy run on the same modern IGA engine that holds the visibility data, so reviewers see why an entitlement is risky at the moment they approve it. That context is what stops reviews from being rubber-stamped.
Veza added access reviews, requests, and provisioning to a platform that began as a data access entitlement tool.
Why companies choose Linx
as a C1 alternative
Risk surfaced proactively
Orphaned accounts, dormant users, and MFA gaps surface without anyone running a query.
Remediation that executes
No-code, dynamic workflows fix what's flagged, without a ticket handoff.
AI across the whole platform
Data refinement, a context-aware assistant on every page, and autonomous action.
Simple and intuitive to use
GRC and security teams operate it directly, no query language required.
All identity types governed, together
One unified policy engine covering humans, non-humans, and agents.
Rated 5/5 on Gartner Peer Insights
Loved by customers and backed by the reviews to prove it.
FAQs
Is Linx a good alternative to C1 (ConductorOne)?
What is the main difference between Linx and C1?
Can C1 and Linx both detect identity risk?
Do you need technical expertise to use Linx?
Do you need technical expertise to use C1?
How do Linx and C1 each handle AI agents and non-human identities?